Previously Convicted Dutch Hacker Arrested in ShinyHunters Odido Probe
Dutch police arrested convicted hacker Pepijn van der Stap in the ShinyHunters probe into…

Latest News
Previously Convicted Dutch Hacker Arrested in ShinyHunters Odido Probe
Dutch police arrested convicted hacker Pepijn van der Stap in the ShinyHunters probe into the Odido breach, which exposed data belonging to…
Fake Email Thread Tricks AI Summarizer Without Hidden Text
Forcepoint X-Labs has published new research showing that indirect prompt injection against AI email summarizers can work without hidden text…
Beyond Account-Level Risk: An Evidence-to-Action Pipeline for Detecting Fraud Rings
Linkage analysis connects accounts, devices and infrastructure to detect coordinated fraud rings that traditional account-level risk controls…
Tech Support Scam Kit Uses Google Ads to Deliver Fake Security Alerts
Google Ads deliver a tech support scam kit that shows fake security alerts, makes browsers appear locked and targets users across hundreds of…
Best Security Awareness Platforms for Personalized Employee Training
Comparing five leading security awareness platforms, based on the level of personalization they offer.
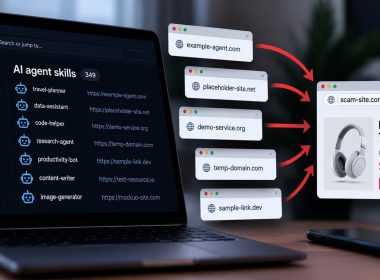
Placeholder Domains Used by 349 AI Agent Skills Found Redirecting to Scams
Manifold Security found placeholder domains cited in 359,000 GitHub files and 349 AI agent skills serving cloaked scam redirects observed on…
ShinyHunters Bypass WAF Rules to Resume Oracle PeopleSoft Attacks
ShinyHunters exploit CVE-2026-35273 in Oracle PeopleSoft using URL encoding to bypass WAF rules, deploy web shells and spread the SIDEEYE backdoor.
5G-Shark Lures Phones to Rogue 5G Cells Without Network Jamming
Researchers have developed 5G-Shark to lure phones onto rogue base stations, collect subscriber IDs, force network downgrades and trigger…
Only 26% of Detected CISA Known Exploited Vulnerabilities Were Fully Remediated
A recent Verizon study found that vulnerability exploitation became the most common initial access vector, appearing in 31% of breaches.…
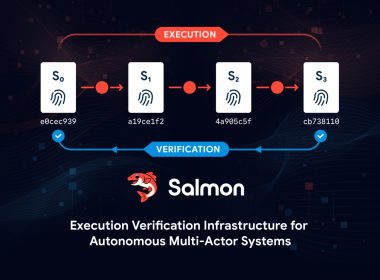
Salmon Introduces Execution Verification Infrastructure (EVI) for Securing AI Agents and Autonomous Systems
San Francisco, USA, 25th September 2026, CyberNewswire
SectopRAT Abuses Legitimate Audio Software Files to Steal PC Data
FortiGuard found SectopRAT hidden in modified audio software files, using staged loading to steal browser data and remotely control infected…
Bitget Confirms $351.6 Million Hack, Suspects North Korea’s Lazarus Group
Bitget confirms a $351.6 million theft, suspends withdrawals and says North Korea's Lazarus Group may be involved as investigators examine the…