
Press play to start listening
The FBI has seized internet domains linked to NightmareStresser, a long-running DDoS-for-hire service accused of helping paying customers launch attacks against targets worldwide.
NightmareStresser had been operating since at least 2022 and was described by the Justice Department as one of the world’s longest-running Distributed Denial of Service (DDoS) services for hire. According to the seizure warrant affidavit cited by prosecutors, the service was used for hundreds of thousands of actual or attempted DDoS attacks against victims worldwide during that period.
Paying Customers Could Launch DDoS Attacks
DDoS-for-hire platforms, commonly called booters or stressers, provide customers with infrastructure for overwhelming websites, servers or other internet-connected systems with traffic.
Rather than assembling their own botnet or attack infrastructure, customers pay the service to direct attacks at selected targets. The resulting traffic can slow services, knock systems offline or disrupt internet connectivity.
The services are advertised through forums, websites and dark web marketplaces, with access commonly sold through online payment services or cryptocurrency. Some operators also sell access to botnets made up of malware-infected devices.
The Justice Department said booter services have been used against educational institutions, government agencies and gaming platforms, as well as other victims in the United States and other countries. However, in NightmareStresser’s case, the agency did not disclose which organizations were targeted nor did it provide the names of individual customers in its press release published today.
NightmareStresser Domains Taken Offline
The seizure means the targeted domains are now under law enforcement control rather than simply being blocked by an internet provider. Visitors to the seized infrastructure are presented with a law enforcement notice displaying the seals of participating agencies.
No arrest or criminal charge against a NightmareStresser administrator was announced alongside the domain seizures. The DOJ announcement instead focuses on disrupting the infrastructure used to provide the service.
The action forms part of Operation PowerOFF, an international effort targeting DDoS-for-hire infrastructure and the people who operate or use the services.
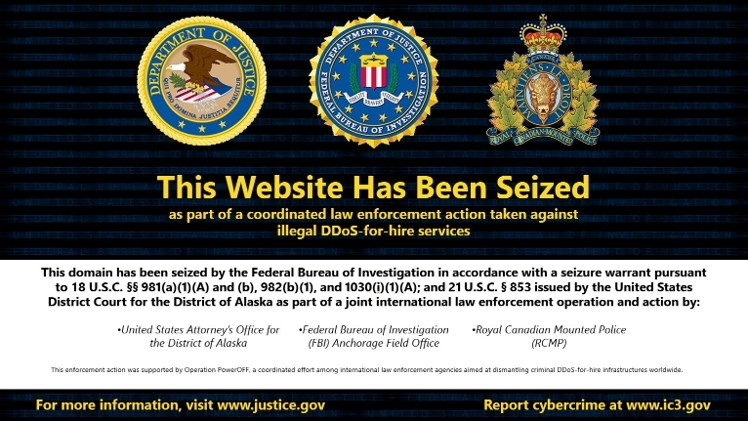
According to the agency, the FBI and RCMP worked together on the latest seizures, while previous PowerOFF operations have involved Europol, U.S. agencies and law enforcement authorities in countries including the United Kingdom, Germany, the Netherlands, Poland, Japan and France.
More Than 100 Domains Seized in Earlier Actions
The NightmareStresser action follows years of law enforcement operations against commercial DDoS infrastructure.
According to the Justice Department, prosecutors and investigators in Alaska and Los Angeles have charged 12 defendants involved in facilitating DDoS-for-hire services and seized more than 100 domains during operations conducted over the past eight years.
In May 2025, U.S. authorities seized nine domains associated with DDoS-for-hire services while Polish authorities arrested four alleged administrators. DOJ said the services targeted in that operation had also been responsible for hundreds of thousands of attacks or attempted attacks worldwide.
Another PowerOFF action announced in April 2026 targeted DDoS services backed by Internet of Things botnets. That operation involved U.S. and international law enforcement agencies, with assistance from companies and organizations including Akamai, Amazon Web Services, Cloudflare, Google, PayPal and The Shadowserver Foundation.


