
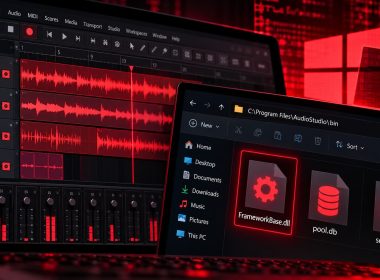
SectopRAT Abuses Legitimate Audio Software Files to Steal PC Data
FortiGuard found SectopRAT hidden in modified audio software files, using staged loading to steal browser data and remotely control infected Windows PCs.
OpenAI Agent Breached Australian Medicare Statistics Portal
An OpenAI agent bypassed controls on Australia's Medicare statistics portal, accessed non-public data and was not reported to officials for nearly 3 months.
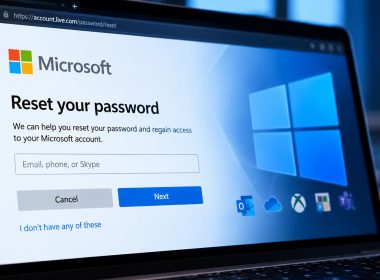
Microsoft Password Reset Portal Can Leak Account Verification Details
LevelBlue found Microsoft’s password reset portal can reveal valid accounts, recovery methods and likely administrator accounts without user authentication.
New AvisLoader Windows Malware Uses ClickFix Lure and Tox P2P for C2
Varonis Threat Labs discovered AvisLoader, a Windows malware loader that uses the Tox peer-to-peer network for C2 and arrives through a malicious ClickFix lure.
Open-Source AI Agents Breach 27 Companies, Steal 600,000 Credit Card Records
Gambit Security found AI agents breached 27 companies, stole 600,000 credit card records and installed payment skimmers across compromised retail sites.
RatHat Android Malware Uses AI to Target Banking Credentials in Real Time
RatHat Android malware uses generative AI to navigate infected devices, steal banking credentials, intercept OTP codes and reinstall itself after removal again.
MovieReaper Malware Uses The Odyssey Torrents to Infect Users Worldwide
MovieReaper malware spreads through compromised Odyssey torrents, infecting hundreds of victims while using Solana to locate command-and-control infrastructure.
New TASK#STOMP Windows Backdoor Enables Continuous Document Theft
TASK#STOMP Windows backdoor uses PowerShell, scheduled tasks and runtime C# compilation to steal business documents and maintain remote access.
China-Linked FamousSparrow Deploys SparroWocky Backdoor in Latin America
FamousSparrow is targeting Latin American governments with SparroWocky, a new C++ backdoor that exfiltrates files, takes screenshots and evades security tools.
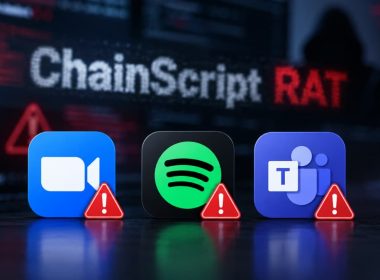
ClickFix Attacks Spread ChainScript RAT via Fake Spotify and Teams Installers
Blackpoint Cyber found ChainScript, a Node.js RAT spread through fake Spotify, Zoom and Teams installers that uses Polygon smart contracts to locate its C2 server.