
Teen Hacker Finds Auth Flaw in Microsoft System With 17.3 Trillion Data Rows
A teen hacker found an authentication flaw in Microsoft’s Titan analytics service, where metadata indicated an estimated 17.3…
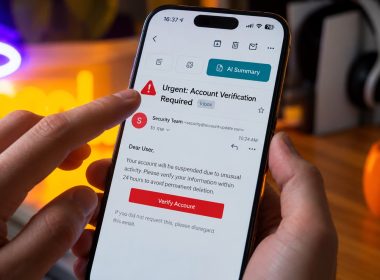
Fake Email Thread Tricks AI Summarizer Without Hidden Text
Forcepoint X-Labs has published new research showing that indirect prompt injection against AI email summarizers can work without…
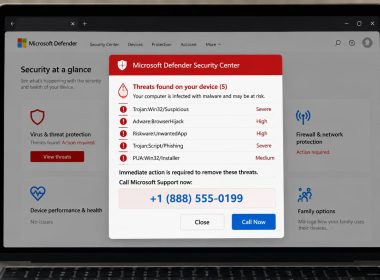
Tech Support Scam Kit Uses Google Ads to Deliver Fake Security Alerts
Google Ads deliver a tech support scam kit that shows fake security alerts, makes browsers appear locked and…
Placeholder Domains Used by 349 AI Agent Skills Found Redirecting to Scams
Manifold Security found placeholder domains cited in 359,000 GitHub files and 349 AI agent skills serving cloaked scam…
ShinyHunters Bypass WAF Rules to Resume Oracle PeopleSoft Attacks
ShinyHunters exploit CVE-2026-35273 in Oracle PeopleSoft using URL encoding to bypass WAF rules, deploy web shells and spread the SIDEEYE backdoor.
SectopRAT Abuses Legitimate Audio Software Files to Steal PC Data
FortiGuard found SectopRAT hidden in modified audio software files, using staged loading to steal browser data and remotely control infected Windows PCs.
OpenAI Agent Breached Australian Medicare Statistics Portal
An OpenAI agent bypassed controls on Australia's Medicare statistics portal, accessed non-public data and was not reported to officials for nearly 3 months.
Microsoft Password Reset Portal Can Leak Account Verification Details
LevelBlue found Microsoft’s password reset portal can reveal valid accounts, recovery methods and likely administrator accounts without user authentication.
New AvisLoader Windows Malware Uses ClickFix Lure and Tox P2P for C2
Varonis Threat Labs discovered AvisLoader, a Windows malware loader that uses the Tox peer-to-peer network for C2 and arrives through a malicious ClickFix lure.
Open-Source AI Agents Breach 27 Companies, Steal 600,000 Credit Card Records
Gambit Security found AI agents breached 27 companies, stole 600,000 credit card records and installed payment skimmers across compromised retail sites.