
Press play to start listening
Cybersecurity firm ESET has identified a new cyberespionage campaign by the China-aligned FamousSparrow group, which is using a new backdoor called SparroWocky against government organizations in Latin America.
SparroWocky is a modular C++ backdoor with capabilities including system information collection, command execution, screenshots, file exfiltration and TCP proxying, along with anti-analysis techniques such as stack spoofing and reflective loading.
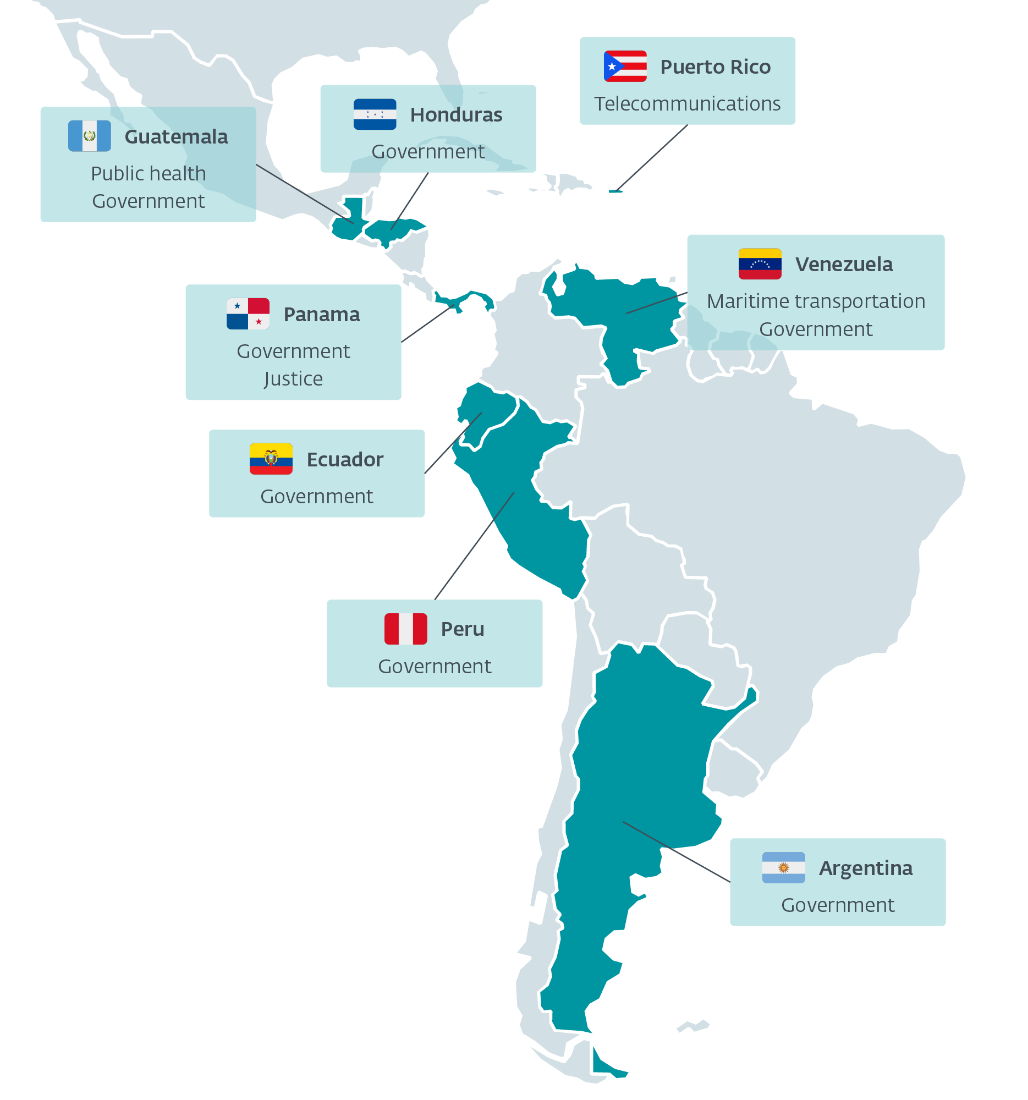
According to ESET telemetry, around 90% of the group’s targets recorded from mid-2025 into 2026 were located in Latin America. ESET observed the backdoor’s deployments against government entities in Argentina, Ecuador, Guatemala, Honduras, Panama, Peru, Puerto Rico, and Venezuela.
Technical Design and Evasion Tactics
ESET named the malware SparroWocky after finding the opening stanza of Lewis Carroll’s poem Jabberwocky inside early samples. The strings appear to come from test vectors included in the Mbed TLS library, which the backdoor uses for secure communications. The malware has largely replaced the group’s older SparrowDoor implant.
“The group has developed SparroWocky, which replaced SparrowDoor as its main implant. While it doesn’t appear to be based on the same codebase, we can see that SparroWocky still shares some of the functionality and concepts that were present in the group’s previous backdoor,” researchers noted in the blog post.
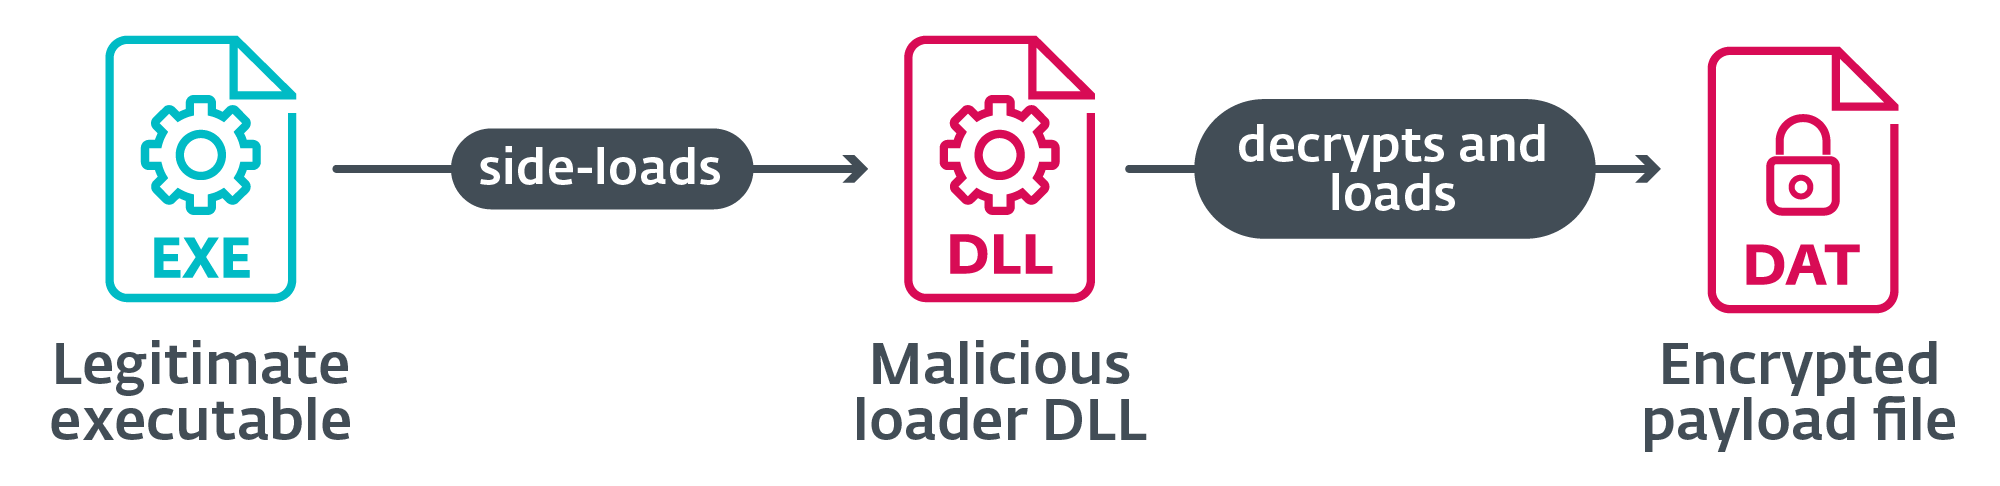
FamousSparrow deploys the backdoor through a trident loader scheme that relies on DLL sideloading. A legitimate executable loads a modified DLL, which retrieves the encrypted SparroWocky payload and configuration data from a .dat file.
The decrypted Portable Executable (PE) payload has its MZ and PE magic values removed before being reflectively loaded into memory. ESET believes this may help evade defenses that rely on simple pattern matching to identify suspicious code in memory.
Analysis of SparroWocky’s Capabilities
The backdoor gives operators extensive control over compromised systems and collects information including hostnames, usernames, domain names, Windows versions and IP addresses. It can also take screenshots, exfiltrate files over TLS with RC4 encryption, execute commands, and act as a TCP proxy.
Moreover, the it can establish persistence through services or registry Run keys. It also uses a COFF Loader component to execute Beacon Object Files directly in memory and SilentMoonwalk to forge call stacks and make monitored operations harder to trace.
FamousSparrow’s Latin America Focus
FamousSparrow has been active since at least 2019. The group was first known for targeting hotels, but later expanded its attacks to governments, international organizations, trade groups, engineering companies, and law firms. ESET publicly documented the group in 2021 after observing it exploit ProxyLogon.
The company says the group’s concentration on Latin America may be linked to growing US interest and China’s economic interests in the region. One targeted Panamanian organization is involved in a commercial dispute over two ports in the Panama Canal area.
ESET researchers suspect the operation may have been intended to obtain advance information about local government decisions, although they acknowledge that the reason for FamousSparrow’s regional focus remains unclear.


