
Press play to start listening
WatchGuard details Overlord RAT attacks using fake Brazilian legal notices, plus Lampion malware and a separate remote access campaign targeting users in Portugal.
Overlord RAT has surfaced in a newly documented malware campaign discovered by WatchGuard that uses fake Brazilian legal notices to trick victims into downloading malicious files. The RAT has previously been reported by Hackread.com in campaigns involving a fake Zoom installer targeting Windows and macOS, and malicious npm packages used to distribute it alongside an information stealer.
In research shared with Hackread.com, WatchGuard Red Cell researcher Euler Neto identified eight fraudulent domains impersonating Brazilian notary offices. The campaign uses obfuscated VBScript, trusted cloud storage services and legitimate Windows applications to deliver the remote access trojan (RAT), while the wider investigation examines two other malware campaigns targeting users in Portugal.
Overlord RAT Exploits Fake Legal Notices
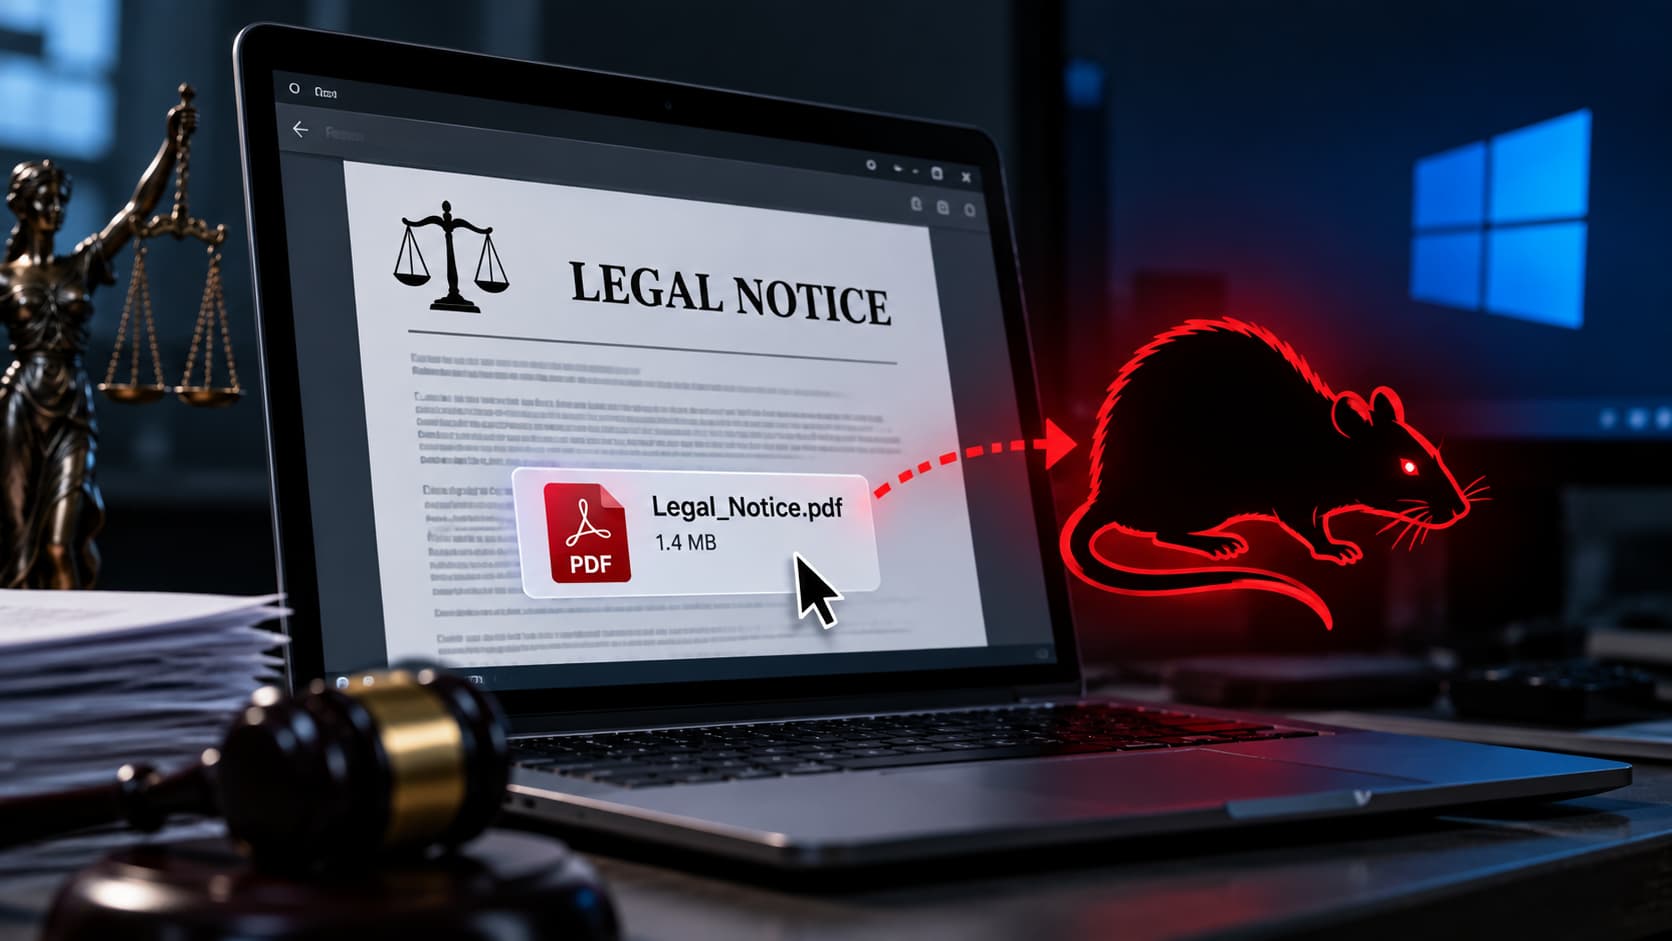
The campaign uses phishing emails posing as Brazilian protest notary offices. The eight domains include 1protestorecife.com and cartorioquintela.com. Links in the emails incorporate valid CNPJ numbers, Brazil’s national registry numbers for legal entities, to make the notices appear legitimate.
Clicking a link downloads an obfuscated VBScript that retrieves additional files from Dropbox or Google Cloud Storage. The scripts use Windows tools such as PowerShell and curl to download payloads, while some modify Microsoft Defender exclusions to reduce the likelihood of detection.
The infection chain also abuses legitimate applications, including Microsoft’s .NET Framework executable ngentask.exe and the VLC media player, to load malicious DLLs. Another variant creates scheduled tasks named “Windows Error Reporting” to maintain persistence.
A Go-based executable downloads an encrypted file named werdata.db and decrypts its contents using the Chaskey cipher in counter mode. Researchers identified the decrypted content as Donut x64 shellcode. The malware then communicates with Overlord RAT infrastructure at 191.96.225.125 and 45.158.8.213, which the report associates with port 5173.
The researchers also found references to Brazilian financial institutions, including C6Bank, PicPay, Banco Inter and Caixa Econômica Federal, in the malware.

Lampion and a Separate Remote Access Campaign
The second campaign delivers the Lampion banking trojan through phishing emails containing ZIP attachments with HTML files. These files retrieve additional scripts hosted on services such as AWS S3 or Google Drive. The heavily obfuscated VBScript stages contain junk code that complicates analysis, while the observed command-and-control infrastructure includes Russian-based IP addresses.
The third campaign uses a Portuguese-language website titled “Download Seguro – Factura” and a fake CAPTCHA to distribute an ISO file. The ISO contains a VBScript, VMware’s legitimate vnetlib.exe and a malicious newdev.dll.
When vnetlib.exe loads the DLL, the malicious code decrypts another 64-bit DLL payload written in Pascal. The payload can execute commands, transfer files, control the mouse and keyboard, and stream the victim’s screen. It also adds a Windows registry entry to maintain access after a system restart.

Although the three campaigns use different infection methods, they rely on familiar tricks to get malware onto victims’ systems, from fake legal notices and phishing emails carrying financial or administrative lures to a bogus invoice-download page.
The use of cloud storage and legitimate applications also gives security teams more than suspicious files to investigate, including unexpected script activity, changes to Defender exclusions and unusual network connections.