
Press play to start listening
The ShinyHunters extortion group has hacked and defaced the dark web leak site operated by the Clop ransomware gang, replacing the site’s content with its own branding and a message directed at visitors.
Hackread.com observed the defacement on Clop’s Tor site on September 19, 2026. The page displayed ASCII artwork associated with ShinyHunters, a link directing visitors to the group’s own site, and the message “rooting your systems since ’19 ;).”
Clop, also written as Cl0p, operates a Tor-based leak site used to name organizations targeted in its data theft and extortion campaigns. The incident is unusual because the target is itself a major cybercrime operation.
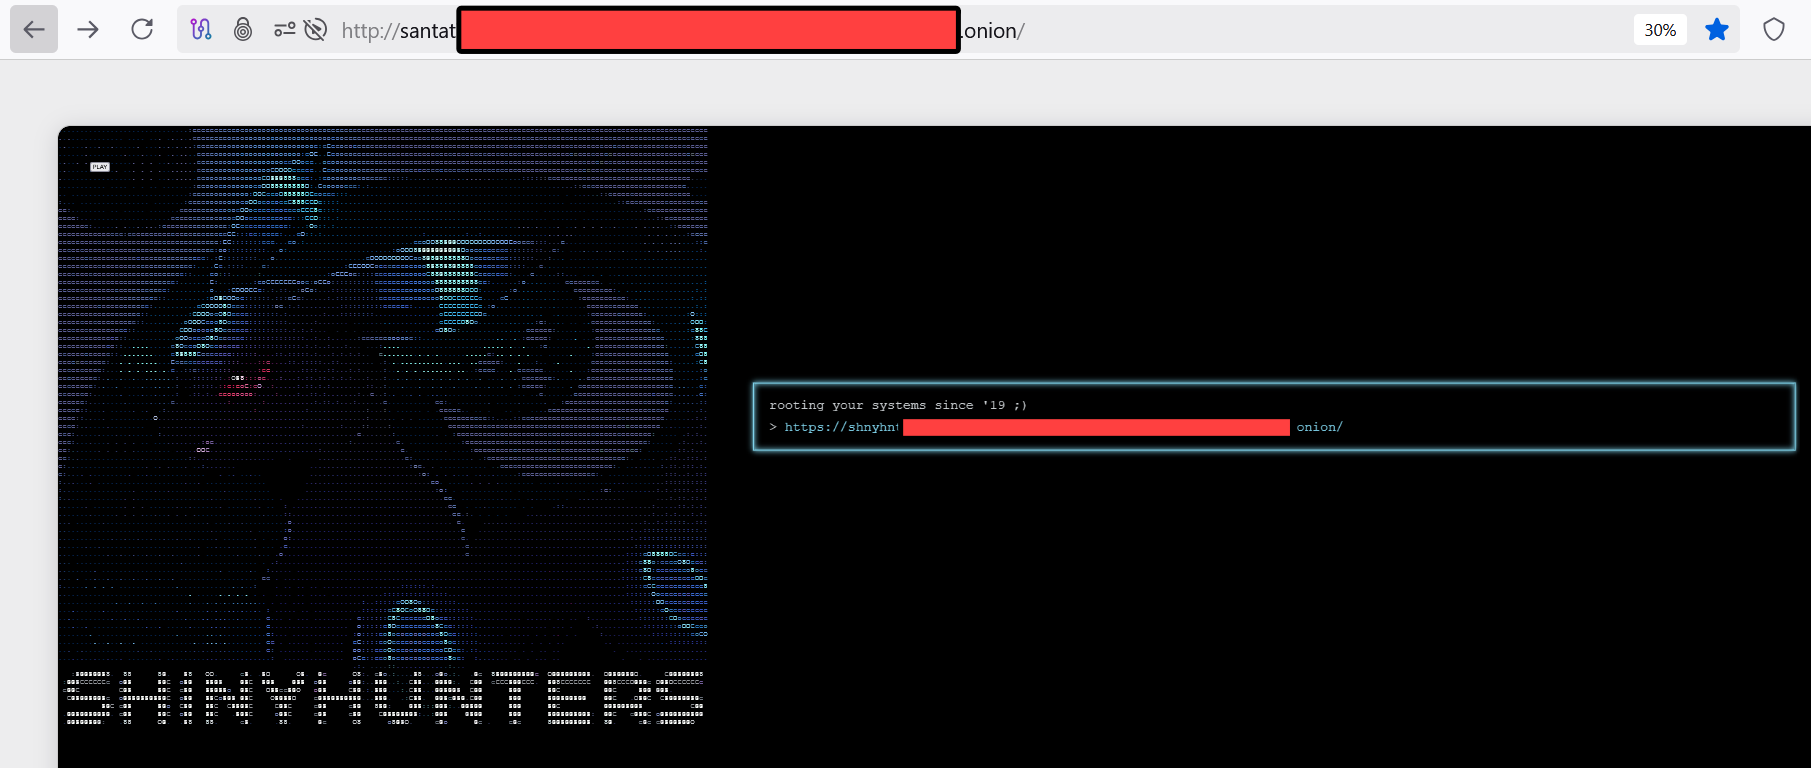
The attack appears to have started on Friday night, September 18. ShinyHunters claims it found an unauthenticated file-upload vulnerability in the Grav content management system used by Clop’s leak site. The compromise later progressed into the full defacement observed by Hackread.com.
Extent of Clop Site Compromise Remains Unclear
The visible defacement shows that whoever carried out the attack gained sufficient access to alter content served through Clop’s onion site. However, the defacement alone does not establish how deeply the underlying server was compromised or what data may have been accessed.
Hackread.com has contacted ShinyHunters directly to ask how the group gained access, whether data was taken from Clop’s infrastructure and whether it obtained control of any additional systems. The group had not responded at the time of publication.
ShinyHunters’ Own Onion Domain Offline
It is also observed that ShinyHunters’ own onion site was unavailable during the incident and had remained down for several hours. The group was asked whether the outage was connected to the attack on Clop or caused by a separate issue.
It is currently unclear why the ShinyHunters site is offline or whether its unavailability has any connection to the Clop compromise. The group had not responded at the time of publication.
Clop’s Onion Site Remains Compromised
Clop’s leak site is an important part of its extortion operation, where the ransomware group names targeted organizations and publishes stolen information when its demands are not met.
Losing control of the site, even temporarily, can damage Clop’s reputation while disrupting one of the main channels it uses to publish victim data and information about its attacks.
Clop has been responsible for some of the largest mass data-theft campaigns in recent years, frequently exploiting vulnerabilities in widely used enterprise file-transfer products. Its 2023 campaign against Progress Software’s MOVEit Transfer exploited CVE-2023-34362 to steal data from exposed systems.
The MOVEit campaign alone affected more than 2,000 organizations and tens of millions of people, with victims spanning businesses, universities and government organizations. Earlier in 2023, Clop also claimed to have stolen data from approximately 130 organizations in just 10 days by exploiting a zero-day vulnerability in GoAnywhere MFT.
The FBI and CISA also linked (PDF) Clop to the MOVEit campaign and noted that the group had previously targeted Accellion FTA using similar tactics.
At the time Hackread.com checked the onion address, the Clop leak site remained unavailable and the ShinyHunters defacement was still being served.


