
Press play to start listening
FortiGuard Labs has identified a Linux backdoor that exploits known vulnerabilities in internet-facing devices and converts infected systems into remotely controlled proxy nodes.
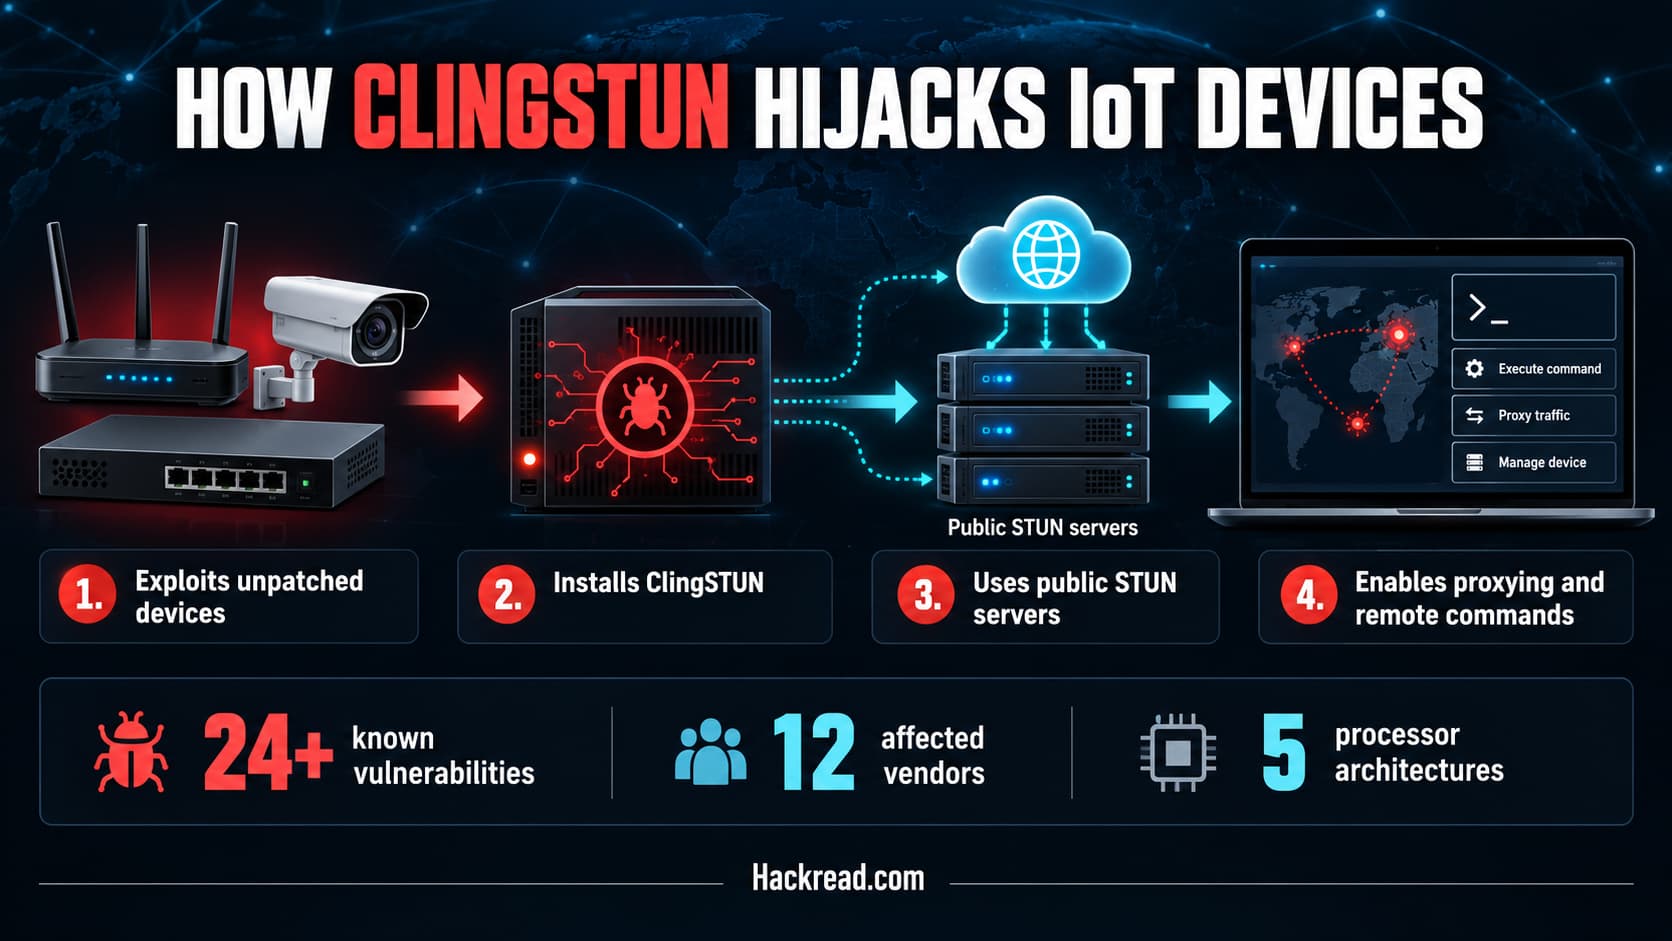
Named ClingSTUN, the malware supports remote command execution, maintains access after a reboot and uses legitimate public STUN servers to communicate through network address translation.
Known Vulnerabilities Used for Initial Access
According to the company’s report shared with Hackread.com ahead of publication on Monday, October 5, 2026, attackers behind the campaign exploited about two dozen vulnerabilities affecting products from:
- Avtech
- D-Link
- EnGenius
- Hytec
- Ivanti
- Lantronix
- Linear
- MeiG
- Realtek
- Sunhillo
- Tenda
- TP-Link
FortiGuard also found seven hardcoded exploits that ClingSTUN can use to spread to other vulnerable devices. Those flaws affect products from:
- China Mobile
- KGUARD
- Linksys
- LB-LINK
- MVPower
- Realtek
- TBK
Downloaders recovered during the investigation could install ClingSTUN on several processor architectures, including AMD x86-64, ARM, Intel 80386, MIPS R3000 and PowerPC. This allows the campaign to target different types of Linux-based IoT and networking equipment.
FortiGuard did not identify the operators, disclose the number of infected devices or name any affected organizations.
Public STUN Servers Used for Connectivity
After infecting a device, ClingSTUN creates a UDP socket and binds it to a randomly selected local port. It then sends standard binding requests to public STUN servers.
STUN, short for Session Traversal Utilities for NAT, is commonly used by services such as VoIP and WebRTC to determine a device’s public IP address and port mapping. ClingSTUN uses the same process to learn how an infected device can receive connections from outside its local network.
Once the binding exchange is complete, the malware periodically sends its group identifier and mapped port list to the same STUN endpoints. FortiGuard did not find a separate registration server handling this part of the communication.
Because the contacted STUN services are legitimate, their presence in network logs does not prove that the services themselves have been compromised or are controlled by the attacker.
Jason Soroko, senior fellow at Sectigo, told Hackread.com that destination reputation alone cannot determine whether such traffic is safe.
“A device does not need to hold sensitive data to be useful to an attacker,” Soroko said. “ClingSTUN lets attackers relay traffic through compromised devices and run commands on them.”
Persistence and Remote Commands
ClingSTUN copies itself into two hidden executable files and adds startup commands to three system initialization scripts. Those changes allow the backdoor to run whenever the device starts.
FortiGuard examined three variants that shared several functions. Each could terminate processes associated with competing malware, interfere with the device’s watchdog timer and listen for specially formed packets from its operator.
Those packets can instruct the infected device to execute commands or begin scanning for more vulnerable systems. In practical terms, attackers can use the device as a proxy while retaining the ability to run code and spread the malware.
A restart will not remove ClingSTUN because its startup entries reload the malware during boot. Soroko advised organizations to examine exposed devices for hidden processes, altered startup files, unexplained UDP connections and repeated STUN keepalive traffic.
Organizations should also identify internet-facing equipment, install available firmware updates and restrict services that do not require public access. Devices that have reached the end of vendor support should be isolated or replaced, particularly when known vulnerabilities remain exposed.


