
Press play to start listening
A Ukrainian man who helped carry out Nefilim and Hive ransomware attacks has been sentenced to 70 months in prison. Artem Stryzhak, 36, participated in operations that encrypted victims’ files and demanded payment for their recovery, including attacks against healthcare organisations during the COVID-19 pandemic.
The US Department of Justice announced the sentence on October 27. Stryzhak, formerly of Barcelona, was arrested in Spain in June 2024 and extradited to the United States in April 2025. He pleaded guilty in December to two computer-crime conspiracy counts.
Paying for Access to Nefilim
Stryzhak joined Nefilim as an affiliate around June 2021, agreeing to give its administrators 20% of his ransom proceeds in exchange for access to the malware.
As Hackread.com reported following his guilty plea, the operation gave affiliates tools to research companies before attacking them. Stryzhak and his co-conspirators used public databases to examine prospective victims’ revenue, size and contact information.
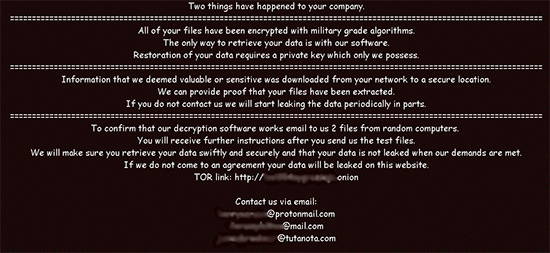
They could then prepare a separate ransomware executable, decryption key and ransom note for each victim. The extortion continued after encryption, with threats to publish stolen information on Nefilim’s “Corporate Leaks” websites if companies refused to pay.
According to the DOJ’s press release, prosecutors described one June 2021 attack in which Stryzhak stole information from an oil and gas transportation company. About a week later, he created email addresses used in its ransom note. His participation in the Nefilim conspiracy continued until at least October 2021.
Hive Attacks Included Healthcare Victims
Stryzhak also became one of Hive’s earliest affiliates. He and his co-conspirators deployed its ransomware against seven victims, including law firms, a dental office and a healthcare provider.
During its investigation, the FBI supplied one of those victims with a decryption key, allowing it to recover encrypted files without paying. Authorities said Hive ransomware collectively attacked approximately 1,500 victims between June 2021 and January 2023, a group-wide figure, not Stryzhak’s individual victim count.
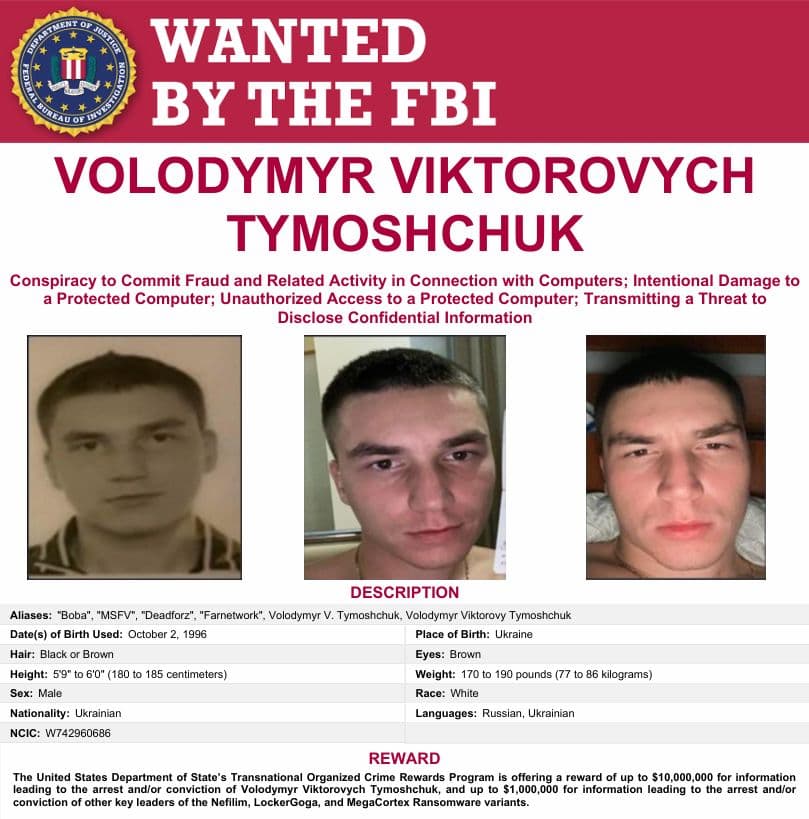
Investigators are still seeking his charged co-conspirator, Volodymyr Tymoshchuk, whom prosecutors identify as a Nefilim administrator. The State Department is offering up to $11 million for information leading to his arrest or conviction, or establishing his location.