
Press play to start listening
The unnamed US executive is separate from Canadian ransomware negotiator Edward Dubrovsky, who was arrested on federal extortion charges.
US federal investigators suspect executives at two ransomware negotiation firms maintained unusually close relationships with ShinyHunters, including one executive who allegedly helped operate the group’s victim-extortion website.
The findings were reported by Brian Krebs of KrebsOnSecurity today, citing sources close to the federal investigation. The report does not identify the US consulting company or the executive suspected of helping run the site because no charges have been announced against them.
Investigators are also examining the conduct of Canadian ransomware negotiator Edward Dubrovsky, who was arrested in Pennsylvania on October 8 on federal cyber extortion and conspiracy charges. His criminal complaint remains sealed, and the specific allegations underlying those charges have not been released publicly.
Investigators Examine Shinywire Operations
The website under investigation, shinywire.com, operated from about May 3 until October 16, 2026. Its homepage displayed a message for companies that had received an extortion email from ShinyHunters, directing them to use the unique link included in the message.
According to Krebs, the site hosted individual extortion pages associated with nearly 100 organisations. The report does not say that the homepage publicly named or listed those victims.
A cached page reviewed by Krebs concerned Intuitive Surgical, a US medical technology company breached in March 2026 after an employee entered credentials through a targeted phishing email. The page encouraged the company to contact ShinyHunters, displayed samples of allegedly stolen files and warned that its data could be published if it did not respond.
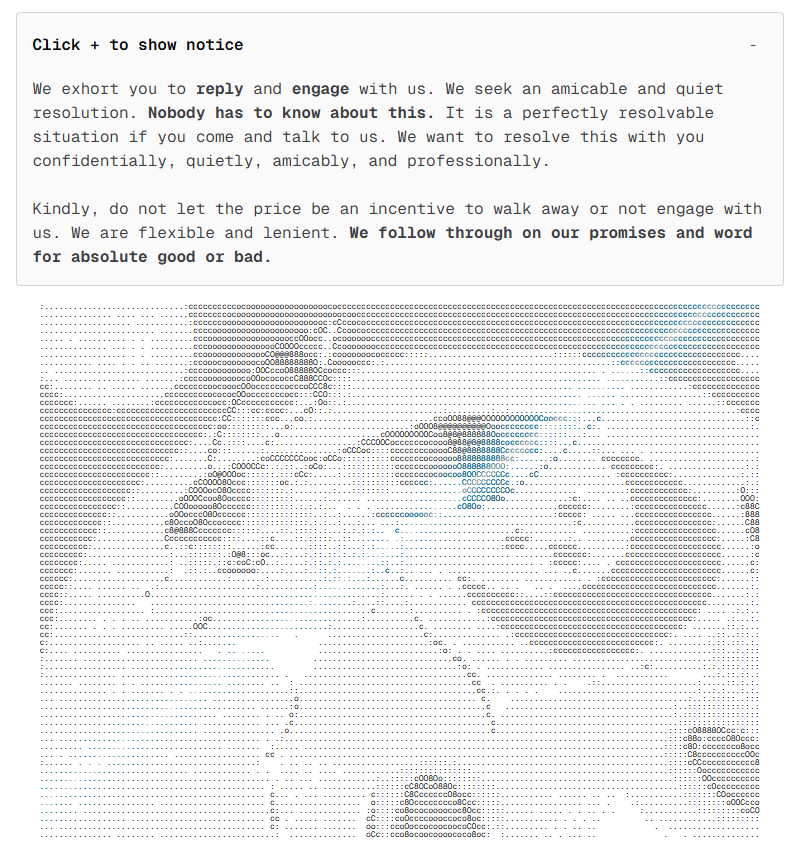
Those victims who did not begin negotiations within seven days could later have their stolen information published through ShinyHunters’ Tor-based leak site. Shinywire was used to communicate demands through private links, while the Tor site was used to release data.
Krebs also reported that investigators believe at least one executive from a large US consulting firm took an active role in operating Shinywire. The company reportedly employs more than 1,000 people but has not been named.
The allegation comes from sources familiar with the investigation. The suspected executive has not been publicly identified or charged, and federal authorities have not released evidence explaining the alleged role.
Messages Reportedly Exposed Negotiator Contacts
Investigators reportedly gained access to recent Signal messages when Dutch police arrested convicted hacker and suspected ShinyHunters member Pepijn van der Stap on September 15.
According to Krebs’s sources, those messages showed frequent conversations between van der Stap, Dubrovsky and at least one executive at the unnamed US consulting firm. The executives allegedly knew details about new ShinyHunters victims before some of the affected organisations learned they had been breached.
One source also claimed Dubrovsky knew ShinyHunters had stolen sensitive FBI personnel data but did not notify the bureau before the group threatened to publish it.
Dubrovsky has not been convicted, and the sealed court record does not publicly confirm these claims. Court filings show that he faces allegations involving conspiracy to impair the confidentiality of information for extortion and interference with commerce through threats.
CYPFER, where Dubrovsky worked from May 2022 until December 2025, has said he served as a managing director and was never a founder or co-founder. He later became associated with CyberSteward, which provides ransomware negotiation and cyber extortion services.
Arrests Follow FBI Jobs Portal Breach
The investigation accelerated after ShinyHunters claimed responsibility for breaching the FBI jobs portal and obtaining personal, medical and employment information belonging to bureau personnel and applicants.
A missed security update reportedly left the Oracle PeopleSoft system exposed, after which the FBI removed a contractor from the assignment. Accenture was later identified as the company managing the platform.
Jordanian authorities had already detained suspected ShinyHunters member Saif al-Din Khader, known online as Rey, on September 29. He was reportedly cooperating with US investigators. The FBI later confirmed multiple arrests but declined to identify every suspect.
The bureau says ShinyHunters has obtained more than $70 million from victims during 2026.
Ransomware Negotiation Firms Face New Scrutiny
Companies hit by data breaches or ransomware attacks often hire negotiators to communicate with attackers, test their claims and reduce payment demands. That access can place negotiators close to victim information, payment decisions and criminal operators.
The ShinyHunters investigation now asks whether people trusted to represent victims also assisted the group pressuring them. Investigators have not publicly established how many negotiators are under examination or whether more charges will follow.
The case follows the separate prosecution of MonsterCloud CEO Zohar Pinhasi, who is accused of secretly paying attackers for decryption keys while charging customers much higher recovery fees. Pinhasi has not been convicted.
Neither case proves misconduct throughout the ransomware negotiation industry. Both cases, however, place the financial relationships between victims, negotiators and cybercriminals under closer examination.


The truly sad thing is most of these ransomed companies (in fact, the majority of companies and governments everywhere) are unethical and break laws left and right. It is hard to say who the worst are in any of this, the ransomers, the ransomed, the ‘negotiators’, or the generally now exceptionally greedy people that expect they deserve things from everyone for free merely because they exist and think they are special. So I can kind of see why these companies pay ransoms; it’s difficult to decide who is worse, their customers, them, or the people that know that those files probably contain incriminating information that, maybe, in some ways, their own customers shouldn’t know about anyway, on account of how eager people are just to sue for things they do to themselves. I left out how corrupt the FBI agents often are, and how the entire security industry chips in to essentially create the things they say they are against, which is a grift/graft/ransom unto itself, and has been for at least thirty years (when Kenyon and Bloodaxe started their Texan ‘security company’ and slid their non-Aeron chairs around, while future dead cows ‘warned’ corrupt politicians who really just wanted more power themselves, as well, about what was to come, then got tons of VC and taught everyone else how to ruin work for everyone in computing, security or not; it only got worse after Y2K).
Everyone seems to be corrupt and extortionist in the world, now.
Seriously, it sucks. And AI/LLMs are just making all of them worse.
It’s not a game. People need to stop ‘playing’ like it is. A lot of these people pay because they are afraid; they are afraid, because most of them are conniving and have things to hide, and are hoping the ransomers don’t know enough to find out what it is.
I’ve never done anything like this, but then again, I’m not, like so many people, going around preventing people from being honest (including myself). I mean, jeez. In what world is an ex-FBI agent suddenly able to go around getting funding for heading multiple security companies? Bad enough most of the people that prosecute big cases often leave and get hired by the same thieving lawyers that go around protecting corrupt companies. This is why white collar people don’t trust law enforcement anymore. It’s not a ‘trade’. The only people getting things are these people swapping favors and money, now.