
Press play to start listening
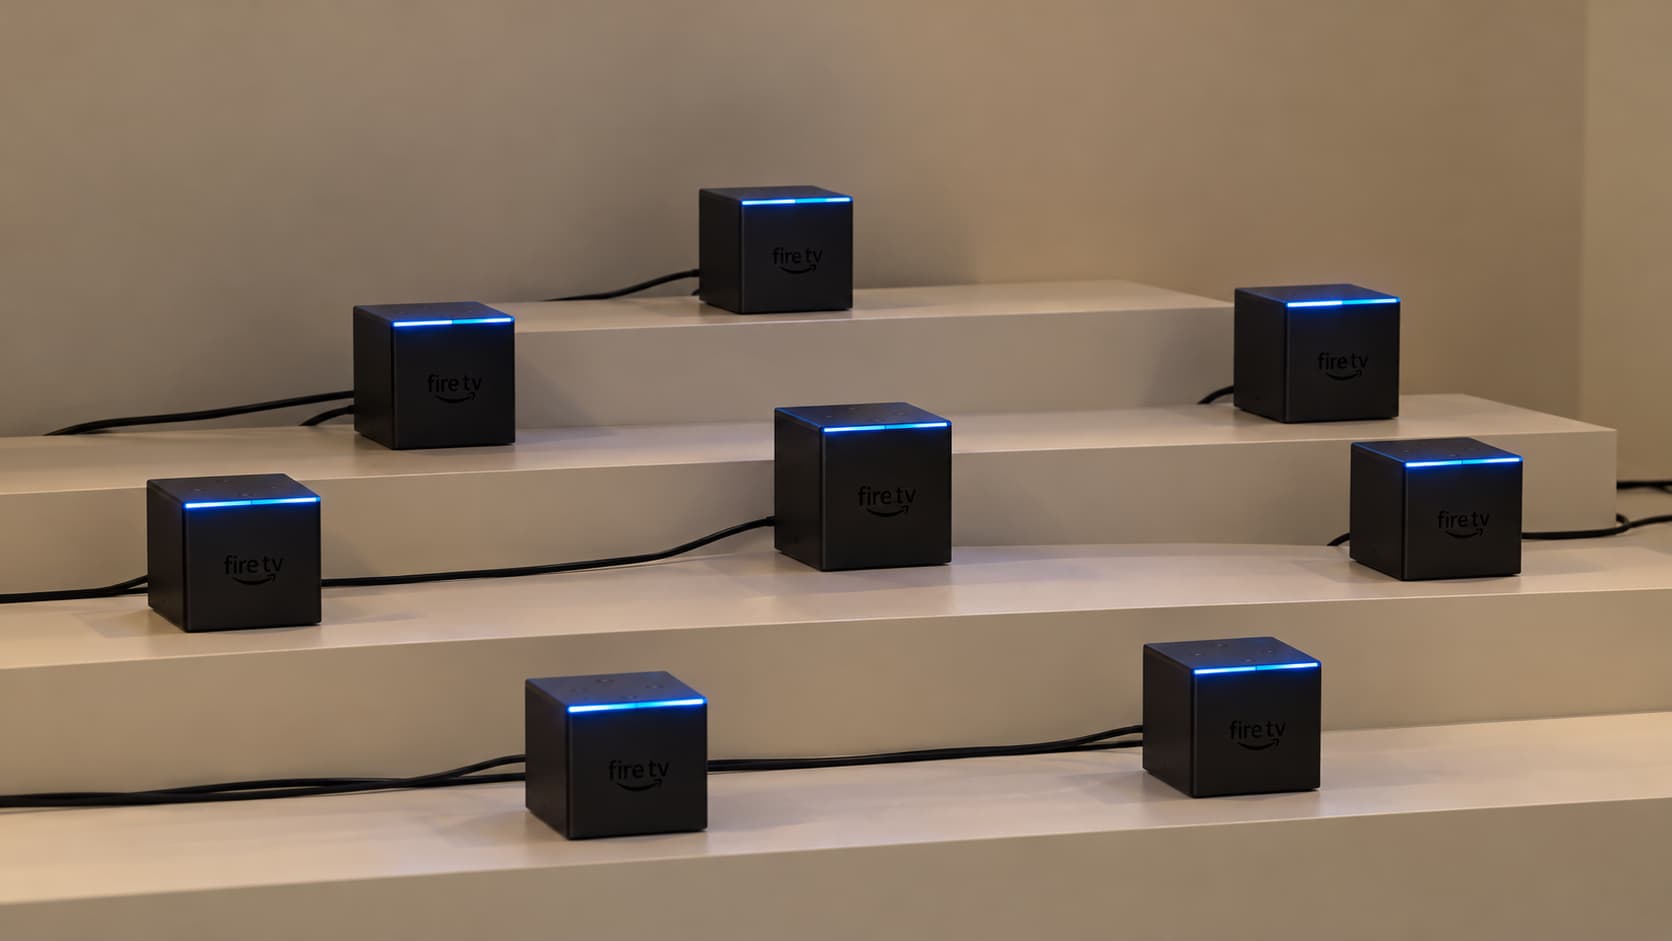
A four-year-old Arm Mali GPU vulnerability can be used to root the third-generation Amazon Fire TV Cube, but its patch status remains unclear.
A vulnerability in Arm’s Mali GPU driver, first disclosed four years ago, has been adapted to gain root access to the third-generation Amazon Fire TV Cube, allowing users to remove Amazon’s software restrictions and install alternative operating systems, according to Cybernews research shared with Hackread.com.
The exploit uses CVE-2022-38181 (CVSS 8.8), a high-severity use-after-free vulnerability in the Arm Mali GPU kernel driver. The bug involves memory that the driver frees while it may still be in use, creating an opportunity to manipulate kernel memory and gain elevated privileges.
Security researcher Man Yue Mo reported the vulnerability to the Android security team on July 12, 2022. His original proof of concept showed how an unprivileged Android process could exploit the bug to execute code in the kernel and gain root access on a Google Pixel 6.
What the Fire TV Cube Exploit Allows
Mo’s technical write-up explains that the process can trigger memory pressure through standard system calls, prompting the driver to free active Just-In-Time (JIT) memory allocations. By manipulating how the kernel reuses that memory, the process can overwrite internal driver structures and take control of kernel space, ultimately gaining root privileges.
Arm released a fix in Mali driver version r40p0 on October 7, 2022. The third-generation Fire TV Cube launched on October 25 that year, but it remains unclear whether Amazon incorporated the fix into FireOS or whether the vulnerable driver remained present on the device.
What Root Access Lets Users Do
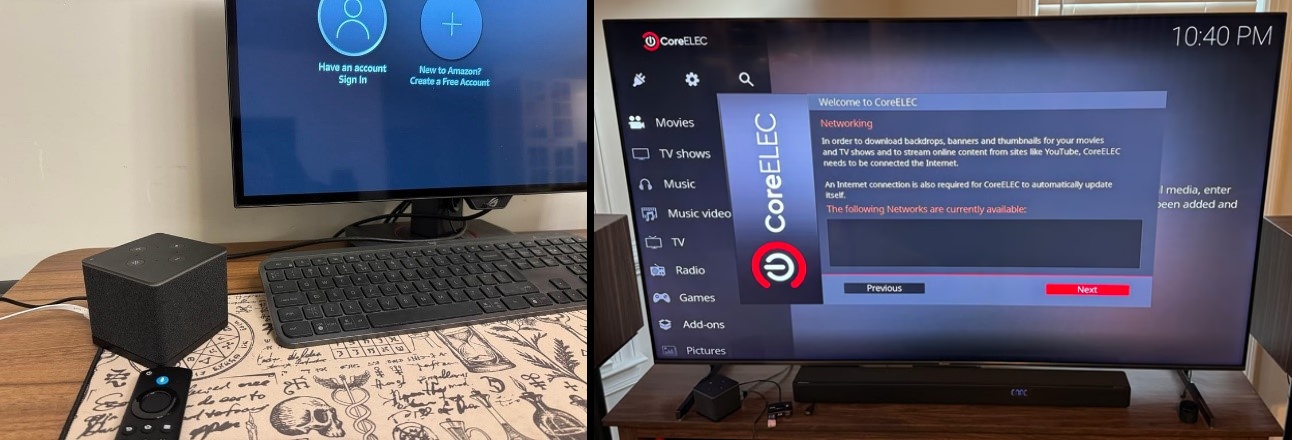
Later, a developer using the alias Pro-me3us shared an adapted version of the exploit on XDA Forums, making it work with FireOS’s 32-bit userspace. With root access, users can install Magisk, replace the Fire TV Cube’s stock recovery system, and load other operating systems.
These include CoreELEC, a Linux-based system built around Kodi for media playback, and EmuELEC, which focuses on retro gaming. Both give users alternatives to Amazon’s standard software, particularly those who want to play local media files or run games on the device.
“For casual Netflix viewers, this might not mean much, but it’s very important for home theater enthusiasts with multi-channel audio setups and the itch to see the content at maximum quality, as the creators intended,” Cybernews noted.
Amazon Says Physical Access Is Required
Amazon told Cybernews that the demonstrated method poses little risk to customers because it requires physical access and deliberate, multiple-step modifications.
“Protecting the security of our customers and devices is our top priority,” an Amazon spokesperson said. “What’s being demonstrated poses little risk to customers; it’s someone modifying a device they own to run unofficial software, which requires direct physical access and a deliberate, multi-step process.”
Since the exploit requires code to run on the device first, the vulnerability alone does not put every Fire TV Cube owner at immediate risk. However, root access could expose data or allow further malicious activity if abused. Cybernews reported no evidence that the exploit was being used in real-world attacks.
Amazon has yet to confirm whether CVE-2022-38181 has been patched in the Fire TV Cube. Until the device’s patch status is clarified, users should be cautious about modifying the system or installing unofficial software.