
Press play to start listening
The escalating dispute between ShinyHunters and the Clop ransomware gang has taken another turn, with Clop apparently regaining the ability to publish on its compromised dark web site and posting a message asking ShinyHunters to make contact.
Hackread.com observed the latest change on September 21, 2026. Clop’s onion address, which had previously been taken over and repurposed by ShinyHunters, displayed a short message from the ransomware gang directed at ShinyHunters.
“Shiny Hunters we trying to reach you Your email does not work. Come online old platform no email,” the message read.
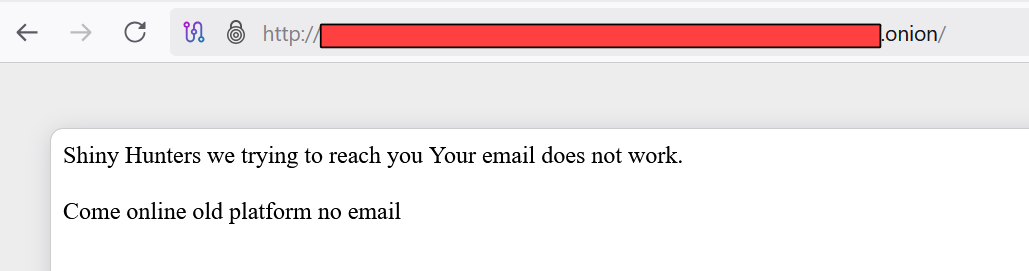
The development comes days after ShinyHunters compromised Clop’s data leak site (DLS) and replaced its normal content with ShinyHunters’ own material. The takeover went further than changing the appearance of the site. During the compromise, visitors accessing Clop’s onion address could download Salesforce-related data that ShinyHunters had also made available through its own leak site.
Hackread.com directly observed the takeover and reported on September 19 that Clop’s normal DLS had been replaced by ShinyHunters content. However, the message alone does not establish whether Clop has fully regained control of the underlying infrastructure or whether ShinyHunters retains access.
ShinyHunters Demands Eight-Figure Payment
Before Clop’s latest message appeared, ShinyHunters had been using the compromised site to issue demands directly to the ransomware gang.
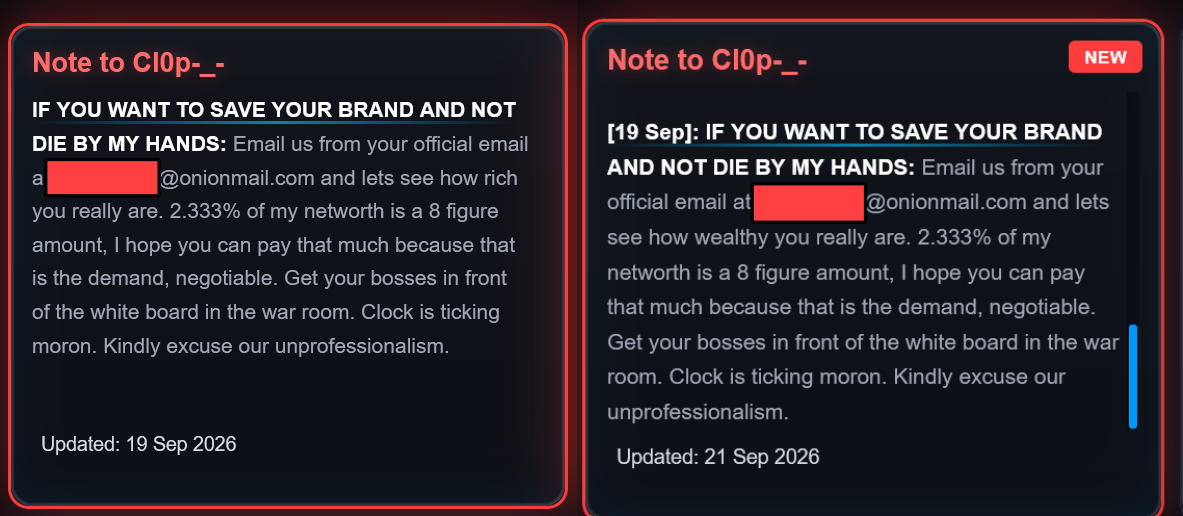
In a September 19 message observed by Hackread.com, ShinyHunters demanded what it described as an eight-figure payment and instructed Clop to contact the group by email. The message included a deadline and a threat directed at Clop if the group refused to engage.
The demand escalated on September 20. ShinyHunters addressed two individuals it identified as “Likhogray & Tarasov” and told them to get their boss, referred to as “j0nny,” to respond.
ShinyHunters said it wanted money that Clop allegedly made from its Oracle E-Business Suite campaign, along with an additional amount and interest. The group also threatened to disclose information it claims to possess about companies that paid Clop, including the amounts involved and Bitcoin addresses allegedly used for the payments.
Hackread.com has not independently verified whether ShinyHunters possesses those records.
Reuters reported on September 21 that ShinyHunters described the incident as part of a longer dispute involving an Oracle E-Business Suite zero-day. According to ShinyHunters’ account to Reuters, it discovered the vulnerability first, while Clop subsequently used the flaw in attacks against organizations. Reuters said it could not independently establish the accuracy of ShinyHunters’ account of how the dispute began.
Public Apology Added to Demands
ShinyHunters updated its message again on September 21, adding another condition. The group said its demands would increase for every 24 hours that Clop failed to engage and demanded that Clop issue a public apology directly to ShinyHunters.
The continuing messages showed that ShinyHunters retained the ability to publish content through Clop’s onion site at that point. That changed later when the ShinyHunters material disappeared and the short message apparently written by Clop appeared in its place.
Clop’s request for ShinyHunters to “come online” indicates that it is attempting to establish contact with the group. The message does not identify the “old platform” it wants ShinyHunters to use.
ShinyHunters Site Outage Was Unrelated
There was another question surrounding the incident after ShinyHunters’ own onion site became unavailable for several hours. Hackread.com contacted ShinyHunters to ask whether the outage was connected to the attack against Clop. The group said it was not.
“Our onion domain is accessible. Please try a new circuit. There was a few hour downtime due to network issues that are not related to the Clop incident. We are dealing with a lot of routine and schedule maintenance on our infrastructure. Thank you.”
ShinyHunters
The site subsequently returned online.
ShinyHunters did not address Hackread.com’s other questions about the extent of its access to Clop’s infrastructure, whether it had taken data from Clop, or whether it controlled additional systems.
A Dispute Between Two Major Cybercrime Groups
The confrontation is unusual because both sides are established cybercrime operations. Clop has operated since at least 2019 and has been responsible for major data-theft campaigns involving vulnerabilities in enterprise file-transfer software, including Accellion FTA, GoAnywhere MFT and MOVEit Transfer.
Its 2023 MOVEit campaign affected thousands of organizations and tens of millions of individuals. More recently, Clop exploited Oracle E-Business Suite vulnerabilities to steal data from organizations using the enterprise software.
ShinyHunters, meanwhile, has been linked to numerous data-theft and extortion operations and has been particularly active in campaigns involving cloud services and enterprise platforms.
For now, Clop is publicly attempting to reach ShinyHunters, while the extent of either group’s control over the compromised infrastructure remains unclear.