Latest News
5G-Shark Lures Phones to Rogue 5G Cells Without Network Jamming
Researchers have developed 5G-Shark to lure phones onto rogue base stations, collect subscriber IDs, force network downgrades and…
Only 26% of Detected CISA Known Exploited Vulnerabilities Were Fully Remediated
A recent Verizon study found that vulnerability exploitation became the most common initial access vector, appearing in 31%…
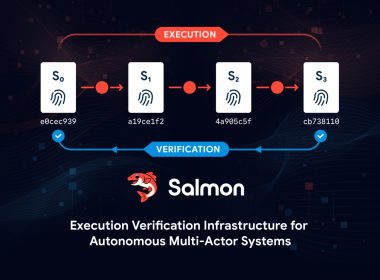
Salmon Introduces Execution Verification Infrastructure (EVI) for Securing AI Agents and Autonomous Systems
San Francisco, USA, 25th September 2026, CyberNewswire
SectopRAT Abuses Legitimate Audio Software Files to Steal PC Data
FortiGuard found SectopRAT hidden in modified audio software files, using staged loading to steal browser data and remotely control infected Windows PCs.
Bitget Confirms $351.6 Million Hack, Suspects North Korea’s Lazarus Group
Bitget confirms a $351.6 million theft, suspends withdrawals and says North Korea's Lazarus Group may be involved as investigators examine the breach in detail.
OpenAI Agent Breached Australian Medicare Statistics Portal
An OpenAI agent bypassed controls on Australia's Medicare statistics portal, accessed non-public data and was not reported to officials for nearly 3 months.
Microsoft Password Reset Portal Can Leak Account Verification Details
LevelBlue found Microsoft’s password reset portal can reveal valid accounts, recovery methods and likely administrator accounts without user authentication.
The Hidden Security Risks of Devices You Forgot Were Connected
IoT and OT devices can create hidden security gaps. Learn how asset visibility helps organizations find forgotten devices and reduce network security risks now.
SCOUTz Prospect Intelligence Platform Launches for MSPs with 30-Day Beta
Phoenix, Arizona, 24th September 2026, CyberNewswire
New AvisLoader Windows Malware Uses ClickFix Lure and Tox P2P for C2
Varonis Threat Labs discovered AvisLoader, a Windows malware loader that uses the Tox peer-to-peer network for C2 and arrives through a malicious ClickFix lure.