Browsing Tag
Malware
2379 posts
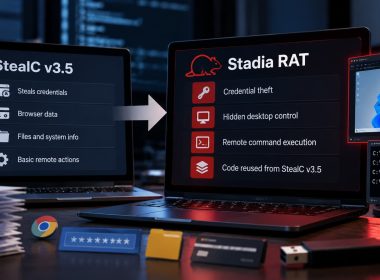
StealC Malware Returns as Stadia RAT After Operation Endgame Takedown
StealC’s seller has returned with Stadia RAT, combining credential theft, hidden desktop control, and remote command execution using…
China-Based BRONZE SANDCASTLE Hackers Abuse Sandboxie to Load Backdoors
Sophos found BRONZE SANDCASTLE abusing legitimate Windows apps to load encrypted backdoors, collect system information and steal Active…
Anthropic Warns Small AI Models Could Power Self-Spreading AI Worms
Anthropic finds small AI models can set up inference servers across different hardware, raising concerns about future AI…
MS Teams Phishing, ClickFix and Shai-Hulud npm Attacks Dominate Threat Report
Ontinue’s 1H 2026 threat report shows attackers increasingly abusing Microsoft Teams, npm packages, device-code logins and blockchain ClickFix…
Powering Proactive Defense: How MSSPs Can Strengthen Threat Hunting Against Ransomware
Disclosure: This article was provided by ANY.RUN. The information and analysis presented are based on their research and findings.
Midnight Mimosa Malware Found Preinstalled on Low-Cost Android Phones
Low-cost Android phones can arrive already compromised, with malware embedded in their firmware before buyers switch them on.
100+ Ukrainian Websites Hacked to Install Lunex Stealer with ClickFix Lure
Over 100 hacked Ukrainian websites used fake Cloudflare checks to install Lunex Stealer and steal browser passwords, tokens and cryptocurrency wallets.
Hackers Exploit 24 IoT Vulnerabilities to Install ClingSTUN Linux Backdoor
Meet ClingSTUN, a new Linux backdoor that exploits IoT vulnerabilities, gives attackers remote command access and turns infected devices into proxy nodes.
Star Blizzard Targets 100+ Organizations with Phishing and RedFlick Technique
Russian group Star Blizzard expands phishing campaigns with a new malware delivery RedFlick technique, using scheduled tasks to deliver the CosmicPulse backdoor.
New CloudSyncD macOS Backdoor Uses Fake Zoom Installer to Steal Passwords
CloudSyncD macOS backdoor uses a fake Zoom installer to steal Mac passwords, bypass Gatekeeper and connect infected devices to remote C2 servers.